Why open canvases need rules
If you read this blog, you probably spend part of your week on an endless board covered in sticky notes, mind map branches, kanban cards, or a half-finished lesson plan. That freedom is the whole appeal of a shared whiteboard, and it is also the risk. A board that anyone can wander into is a board where a client roadmap, a student roster, or a pricing draft can leak without anyone noticing.
Remote teams and educators face the same basic problem from different angles. A product team wants contractors to comment without rewriting the backlog, while a teacher wants students to add ideas without touching the answer key. Neither wants to spend a morning managing permissions, so the goal is a setup that is strict where it matters and invisible everywhere else.
There are three realistic ways to get there, and each trades convenience against control. Before comparing them, it helps to see the wider picture, including the device layer that board settings cannot reach. For that deeper end of the spectrum, a guide to managed endpoint detection and response EDR explains what monitoring on laptops and phones actually involves, which matters once your boards hold anything sensitive.
The threat is not abstract. According to Ic3, losses reported to the FBI’s Internet Crime Complaint Center continued to climb in 2025 and passed the $20 billion mark, with business email compromise among the largest categories. Many of those cases start with a stolen login or a convincing message, which is exactly how a shared link or a weak account ends up exposing a workspace.
| Measure | Figure |
|---|---|
| Complaints received by the FBI’s IC3 | 1,008,597 |
| Reported internet crime losses | About $20.877 billion |
| Reported losses the year before | About $16.6 billion |
| Year-over-year rise in losses | 26% |
| Average reported loss per complaint | About $20,699 |
Invite-only boards with named roles
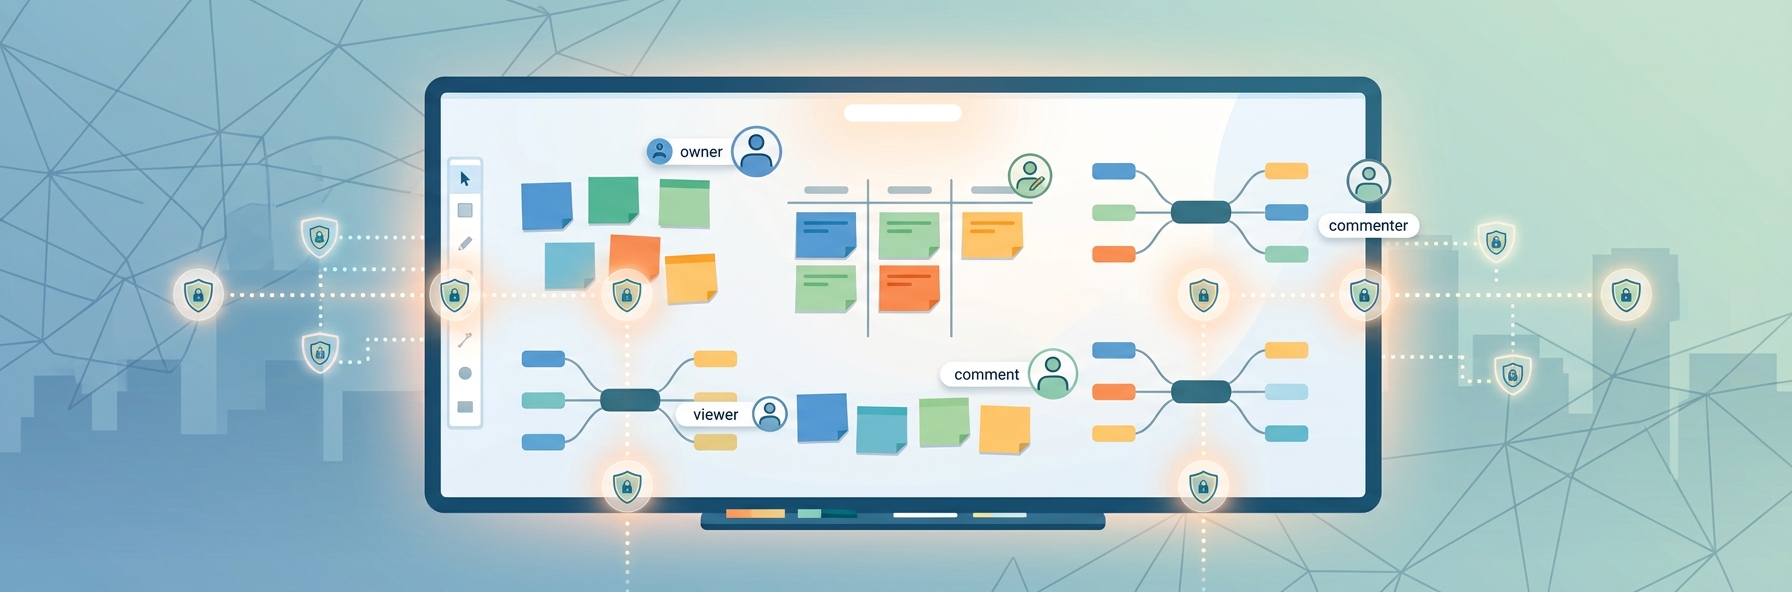
The most familiar approach is to add people by email and give each a role, such as owner, editor, commenter, or viewer. It maps neatly onto how teams already think. A project lead edits, a stakeholder comments, and a guest from another department only views the kanban board.
The strength here is accountability. Every change traces to a named person, and removing someone when a contract ends takes a single click. The weakness is upkeep, because roles drift as projects change, and a former intern with editor rights on a dozen boards is a common finding in any audit. Schedule a quarterly review of who can do what, and default new invitees to the lowest role that lets them do their job.
This model also suits classrooms well. A teacher stays owner, students join as editors on a brainstorm board, and parents or administrators get view-only access. It takes a little setup time, but it avoids the awkward moment when a stranger appears on a group mind map.
Link-based sharing with passwords and expiry
Sometimes inviting by email is too slow. A workshop with forty participants, a one-off client review, or a public brainstorm all call for a link. Link sharing is fast and friendly, since nobody needs an account or a waiting period before they can add a sticky note.
The tradeoff is that a link is a key that can be forwarded, pasted into a chat, or indexed somewhere unexpected. You can soften that with a password, an expiry date, and view-only defaults, then switch the link off once the session ends. Even so, you cannot say with certainty who used it. For low-stakes ideation that is fine, but for anything containing personal data or unreleased plans, treat a link as a convenience rather than a control.
Identity and device-backed access
The strictest approach ties access to who someone is and what they are using. Single sign-on and multi-factor authentication make a stolen password far less useful, and organization-managed accounts mean offboarding someone from the company also removes them from the boards. Layered on top is device security, such as disk encryption, screen locks, and managed endpoint protection that watches laptops for suspicious behavior.
This is the heaviest option, and for a three-person startup it may be overkill. It also needs someone to administer it, whether an internal IT lead or an outside provider. But if your boards hold customer details, student records, or financial planning, it closes the gap the other two approaches leave open, because a perfectly configured board is still exposed when the laptop opening it is compromised.
Picking a mix that fits your team
Most groups do best with a blend rather than a single method. Use named roles for the boards that matter, time-limited links for workshops and open sessions, and stronger identity checks wherever sensitive material lives. A simple sorting habit helps: label each board as public, internal, or restricted when you create it, and let that label decide the sharing settings.
If you are still shaping how your group works together, ideas for team collaboration can help you decide which boards deserve tighter rules in the first place. Start small, review access regularly, and keep the process light enough that people actually follow it. Security that gets in the way tends to get bypassed, while security that fits the workflow quietly protects the work.
Published: October 17, 2026